Capture the Flags
Andrew Rodero’s CTF number two
I wanted to test and see what the tool I’ve been designing is actually capable of in a capture the flag type environment. So I went and solved three of Andrew Rodero’s CTF challenges start to finish (without looking at the answers beforehand, so its more realistic!), just to see. The first seemed like a peice of cake, so I decided to go with the second challenege and do a little walkthrough on it, using the tool. If you would like to follow along, I did a full screencast of my solving of the challenge, and it is embedded below.
How I went about it
So first off I hit stats, and take a look at all these short streams on different ports. They seem to have little quotes from the movie “Wargames” in them. So thats kind of interesting, but I didn’t get the joke yet until I got a little further in. Then went and switched to Entities view so I could really develve down through the protocols, and see if I could find anything else intersting. I found a FTP transfer that wasn’t just movie quotes, so I checked that out in Conv’s Decoder. I wanted to see if anything was interesting about the network typology itself the pcap came from, so I also went and brougth up the Subnets and Threat Intel tabs breifly, but I didn’t see anything particuulaly intersting there, so I quickly proceeded to back back out and check out the data that went over FTP.
So I load the data up in the transferred text file that says something like “global thermonuclaer war” (another wargames reference!)… in the file is just a plain link. Ok, well that may be interesting. I added it to the session keystore for future reference, and proceeded to open it in a browser.
It appears to be Google Docs document, once the URL shortener forwards me. Neat… it looks like Tic Tac Toe! Yet another wargames reference, now I’m starting to chuckle.
Progress
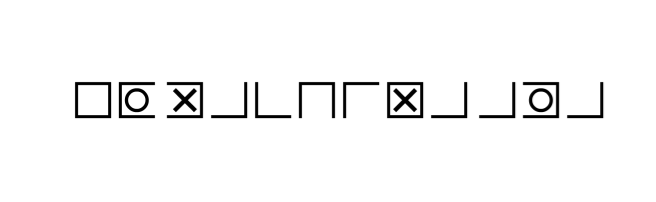
I saved the file to a text format file, then imported into PacketSntich’s Conv Workspace. Now I think I see waht’s happening here! It resolves to char(), character references! So I convert it from CHAR to HEX and….
Boom.
EXMACHINA AVA
For those intersted, this is the Analysis Tab’s Summary of the Session, as drawn up entirely by PacketSnitch’s AI.
Good game, thanks for playing!
This IMO was a successful venture into capture the flags using PacketSnitch. I’ll probably add some new entires soon, as I have the time.